Wyndham App Exposed Customer Data Through a Password Hidden in Its Code
A researcher using AI tools found a credential in the hotel group's Android app that opened a Salesforce-hosted database holding names, emails, member numbers and login tokens.
By Nakoda News Desk
·2 min read
Prefer Nakoda News on Google
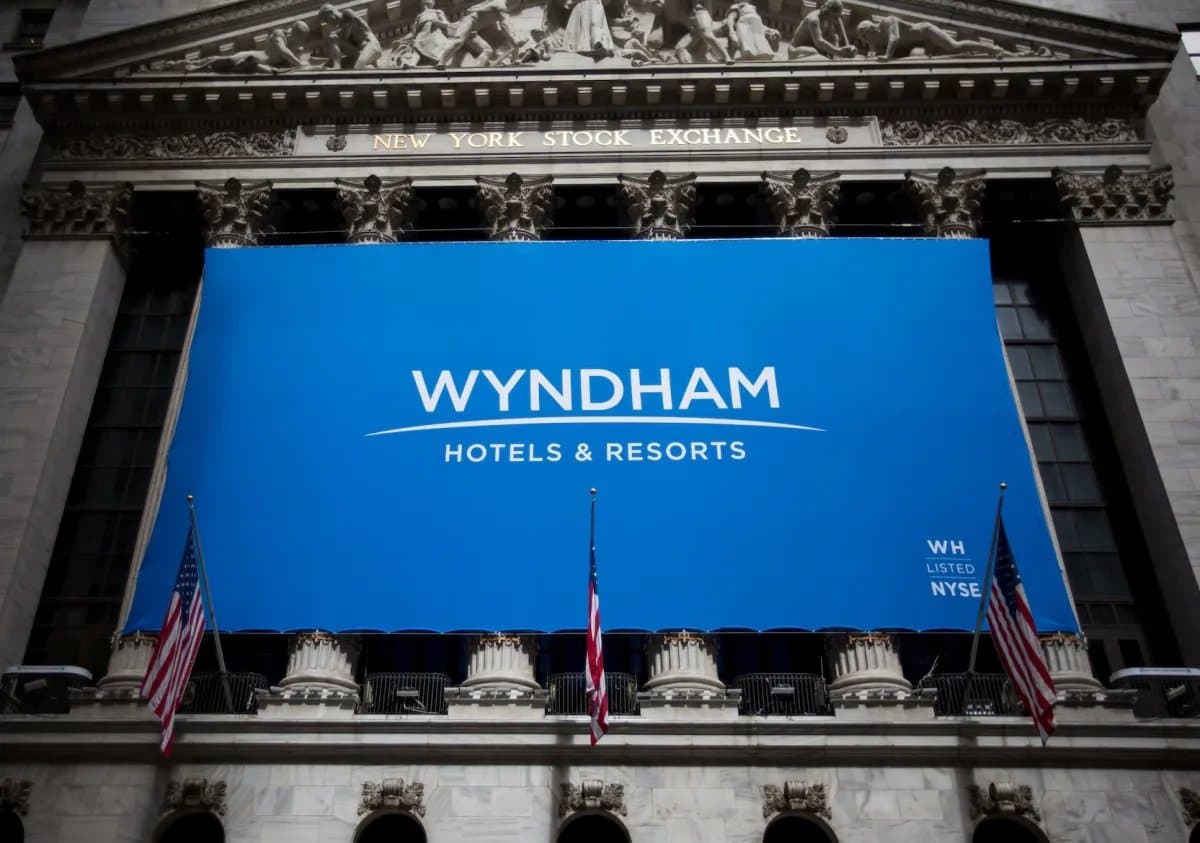
Wyndham Hotels & Resorts has acknowledged a security lapse after a researcher found a password embedded in its Android app that gave access to an internal customer database, TechCrunch reported.
Robert Wiggins, a security researcher at What Security, told TechCrunch that the credential opened a database hosted by Salesforce containing customer names, email addresses and Wyndham member numbers. The database also stored login tokens, known as JWTs, that keep customers signed in to the app, as well as internal company files and documents. Wiggins said the database held millions of entries but he could not determine how many customer records were exposed. Wyndham says it has some 129 million enrolled rewards members.
The flaw matters beyond one hotel chain because Wiggins said he found it with AI tools that can scan thousands of lines of decompiled app code every second for simple weaknesses such as hardcoded credentials. It is his second such public find in two weeks, after a near-identical flaw in Applebee's app that exposed customer data. Hardcoding a password into publicly distributed software lets anyone who downloads it extract the credential, and such flaws are often given the maximum severity rating.
Wiggins said Wyndham had no channel for reporting security flaws, and he asked TechCrunch to alert the company. The credential was revoked soon after the publication contacted Wyndham's security staff.
"Our team has taken steps to address the issue," a Wyndham spokesperson told TechCrunch, adding that the company's security teams had "no evidence of any unauthorized access." The spokesperson would not say whether Wyndham had server logs that could show whether anyone accessed the data before the discovery, how long the password had been in the app, whether customers would be notified, or whether the company would disclose the incident to the US Securities and Exchange Commission, which requires public companies to report material cybersecurity incidents.
Michael Francess, Wyndham's cybersecurity director, said researchers could report issues by email, but the company would not say whether it plans to set up a formal vulnerability disclosure programme. Wiggins said he was glad the issue was fixed, but warned that without visibility into past activity, a malicious actor could have taken large amounts of customer data.
Sources
- TechCrunch · Hotel giant Wyndham exposed customer data after app security lapse
Produced with AI assistance from the sources above. How we work
By
Nakoda News Desk
Nakoda News covers AI and business. Every story links the sources it draws on; how we work is set out in our editorial standards.
Related coverage
- Companies
Nvidia's Board Faces Governance Test as Gensler Says Huang Appears to Have Misled Public
3 hours ago · 3 min read
- Companies
Skydance Breaks Down $6 Billion Cost-Savings Plan, Citing AI and Back-Office Cuts
3 hours ago · 2 min read
- Companies
Jensen Huang Pulls Out of ElevenLabs Summit and Anthropic CEO Forum as Nvidia Inquiry Runs
4 hours ago · 2 min read
- Companies
Lead Director Stephen Neal Expected to Play Central Role in Nvidia's Huang Inquiry
4 hours ago · 2 min read
- Companies
Fervo's Contracted Revenue Jumps to $11.9 Billion on 396MW Google Geothermal Deal
4 hours ago · 3 min read