DIFC Proposes Three-Tier AI Rules That Would Recognise EU, ISO and Singapore Certificates
The draft AI Adequacy Protocol would score AI systems that handle personal data on four factors, and firms already certified elsewhere would only be assessed on Dubai-specific gaps.
By Nakoda News Desk
·3 min read
Prefer Nakoda News on Google
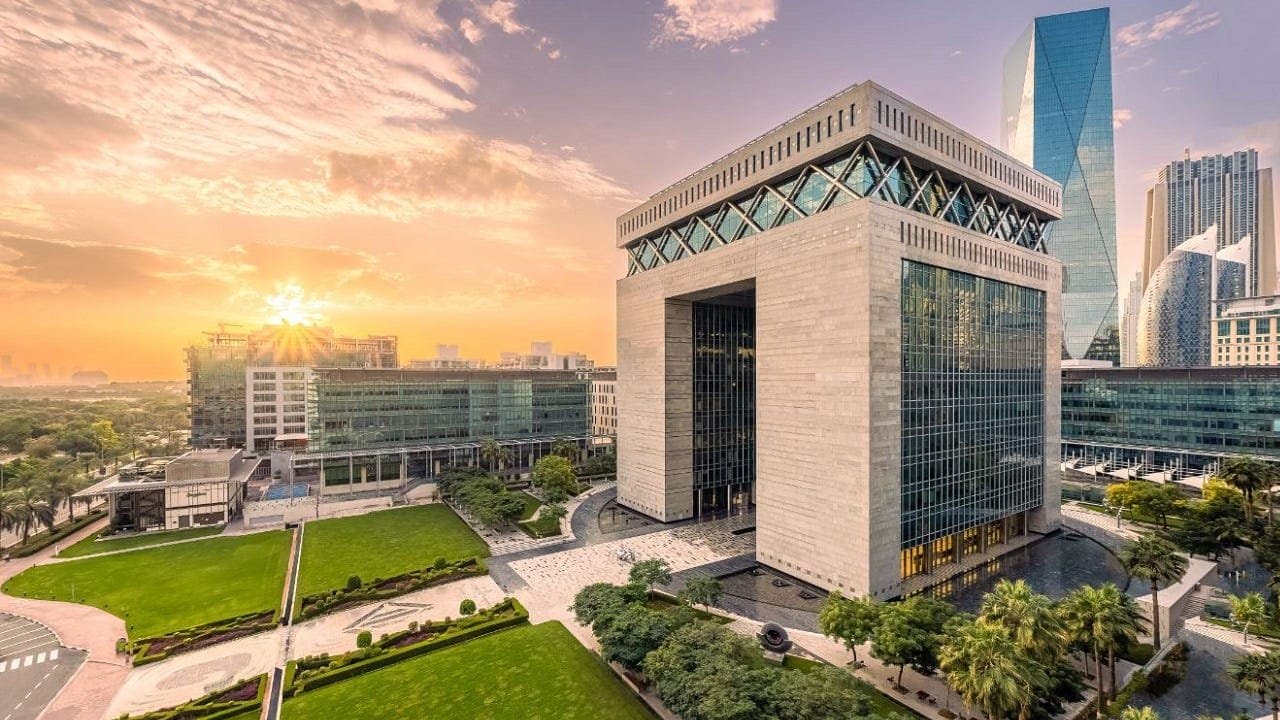
The Dubai International Financial Centre has opened a public consultation on a draft framework that would sort artificial intelligence systems handling personal data into three risk tiers, each with its own certification and oversight rules.
The proposed AI Adequacy Protocol would cover how AI systems that process personal data are developed, deployed, procured and used inside the financial free zone, according to a draft outline released with the consultation and described by Middle East AI News. The part with the most commercial weight is a reciprocity mechanism. Companies that already hold an EU CE marking, ISO 42001 certification or Singapore's AI Verify could ask for those credentials to be mapped against DIFC requirements. An accredited certification body would then identify the gaps, and a shorter assessment would cover only the elements specific to the DIFC.
For companies selling AI products across several jurisdictions, that would mean not having to start certification from scratch in Dubai. The draft also sets out how DIFC would compare its own rules with those of the EU, the UK, Singapore and selected US states. The DIFC Commissioner would keep an equivalence registry, rating each jurisdiction's compatibility as high, moderate or low against eight criteria.
How Systems Would Be Scored
Under the draft, each system would be scored from 1 to 3 on four factors: data volume, decision impact, autonomy and data sensitivity. A combined score below 6 would be classed as Standard, 6 to 9 as Enhanced, and 10 or more as Critical. Any system that makes legally significant automated decisions would be treated as Critical whatever its score.
Standard systems would follow a self-declaration route, with an accredited certification body carrying out the assessment and certification lasting three years. Organisations running Enhanced or Critical systems would have to appoint an Autonomous Systems Officer. Critical systems would also need quarterly monitoring metrics, and larger organisations would need board-level oversight.
Some sectors could face extra requirements. The draft gives examples: model risk management and fair lending analysis in financial services, clinical validation in healthcare, and human review of rejected candidates in recruitment.
Who Carries the Blame
The protocol sets out separate duties for providers, operators and deployers, but places ultimate accountability on deployers, with a deeming provision that attributes a system's actions to them. Deployers would also have to keep track of their supply chain and hold model cards for third-party components, which would matter for the many financial firms that build on models supplied by outside AI labs.
Enforcement would run through five levels, from guidance for minor documentation faults up to revocation, penalties and referral for prosecution where there is harm or persistent violation. Appeals would go first to an independent panel and then to the DIFC Courts. DIFC also plans a Regulation 10 Accelerator to test the new approaches over periods of 6, 12 or 18 months.
The draft was prepared by a sub-group on AI adequacy within the Regulation 10 Advisory Committee. It builds on Regulation 10, which the DIFC Commissioner of Data Protection enacted on 1 September 2023 to govern how autonomous and semi-autonomous systems, including AI, process personal data, and on the DIFC Data Protection Law of 2020. Full enforcement of Regulation 10 began in January 2026. Earlier this year the centre ran a separate 30-day consultation, from 18 June to 18 July, on amendments to its data protection regulations covering AI systems, certification and data governance.
DIFC is collecting feedback through an online survey that it says takes about 10 minutes. The material released with the consultation gives no closing date, and the protocol remains a draft that could change before adoption.
Sources
- Middle East AI News · DIFC opens consultation on three-tier AI rules
- Gulf News · DIFC opens 30-day consultation on AI and data protection rule changes
Produced with AI assistance from the sources above. How we work
By
Nakoda News Desk
Nakoda News covers AI and business. Every story links the sources it draws on; how we work is set out in our editorial standards.
Related coverage
- Policy
UAE Bans Backpacks for Delivery Riders and Sets E-Scooter Permits in 2027 Traffic Rules
5 hours ago · 2 min read
Policy Australia to Create AI Safety Regulator After OpenAI Agent Breached Medicare Portal
5 hours ago · 2 min read
Policy Google Says Gemini's Human Reviewers May See Excerpts of Users' Gmail and Drive Files
6 hours ago · 2 min read
Policy Elvis Presley and Eminem Rights Holders Sue Suno Over AI Training and Voice Imitation
7 hours ago · 3 min read
- Policy
Trump Says Huang Told Him He Had 'No Idea' Woman Was a Spy, Stays Vague on When He Knew
7 hours ago · 2 min read