Landmark Group's Shukran Says Members' Personal Data Was Accessed in Breach
Names, contact details and dates of birth were exposed, the loyalty programme told affected customers, though it says card data, passwords and points balances were untouched.
By Nakoda News Desk
·2 min read
Prefer Nakoda News on Google
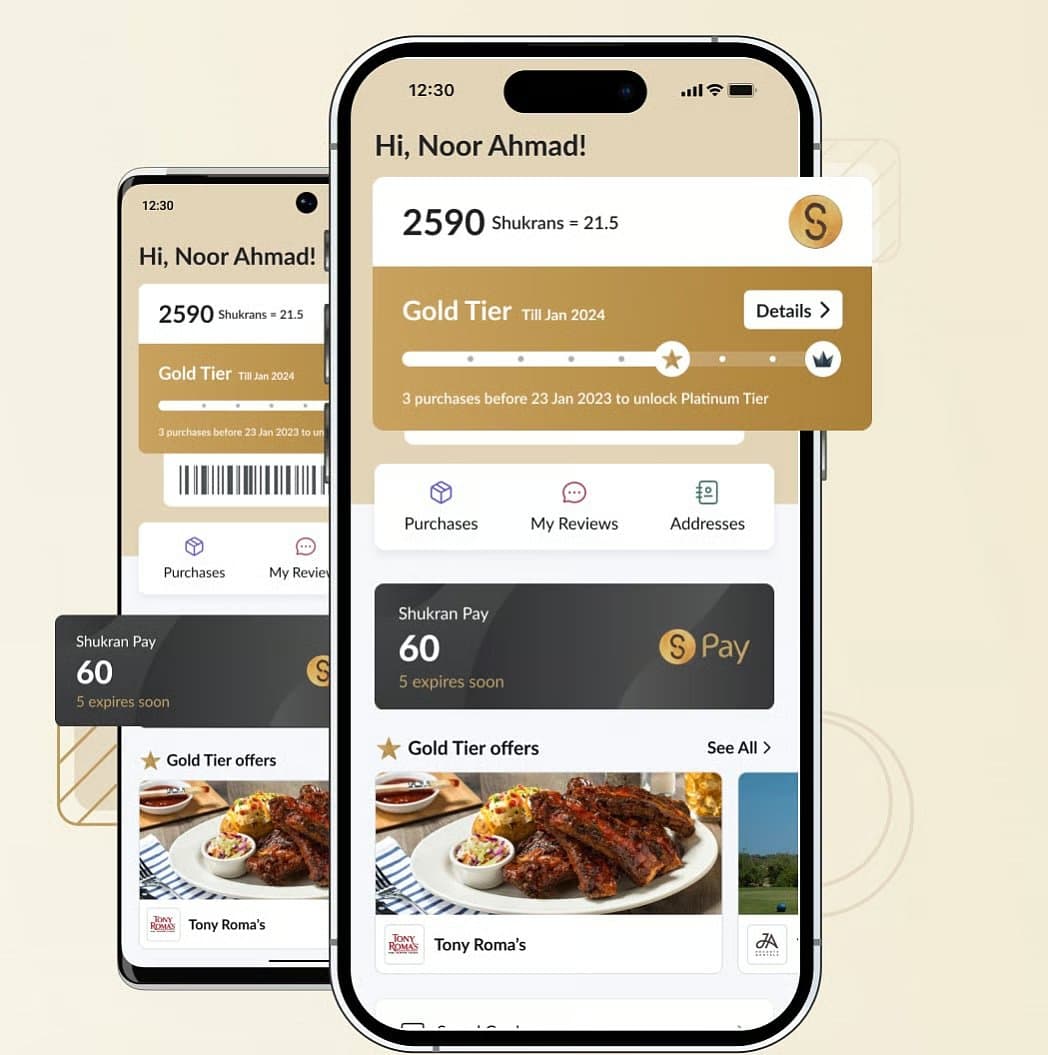
Shukran, the loyalty programme run by the retail and hospitality group Landmark Group, has told members that an unauthorised party gained access to some of their personal information. The data includes names, contact details and dates of birth, according to an alert the company sent to affected customers.
The programme has a large membership in the Gulf. Shukran points can be earned and spent across Landmark chains including Centrepoint, Max Fashion, Home Centre, Babyshop, Splash, Lifestyle, Shoemart and Emax, and the group trades across the GCC, the wider Middle East, Africa and parts of Asia. Shukran has not said how many members are affected, when the intrusion happened or which countries' records were involved.
The company said it identified the incident, moved immediately to contain it and informed the relevant statutory and law enforcement authorities. It said its investigation is continuing. Customers who received the alert should assume their information is among the records involved, it added.
Shukran said debit and credit card numbers were not exposed because it does not store them on its systems. It also said passwords were unaffected because they are protected and not kept in readable form. Points, balances and wallets were not touched, it said, and the app and loyalty services are running normally.
"Protecting your information is our responsibility and one we take extremely seriously," the company said in a question-and-answer page it published about the incident.
Even without card or password data, the stolen fields are useful for impersonation. Shukran's own guidance points to that risk. It told members to treat unexpected calls, emails, text messages or WhatsApp messages that mention Landmark Group, Shukran or any of its brands with suspicion, especially those that create urgency, carry unexpected links or attachments, or offer refunds, prizes or bonus points. Members should never give out passwords, one-time passcodes, banking details or identity documents to anyone who contacts them, and should use a unique password for their Shukran account, the company said.
Shukran said it only asks for one-time passcodes at a shop counter or inside the Shukran app, never by phone or email. It has not said whether it will notify more members as the investigation goes on.
Sources
- khaleejtimes-english · Shukran members’ personal data accessed in data breach, but card details safe
Produced with AI assistance from the sources above. How we work
By
Nakoda News Desk
Nakoda News covers AI and business. Every story links the sources it draws on; how we work is set out in our editorial standards.
Related coverage
- Companies
CoreWeave CEO Intrator Halts His Share Sale Plan After Selling $794 Million of Stock
10 hours ago · 2 min read
- Companies
Apple Is Closing Its Support Community Forums on November 20
11 hours ago · 1 min read
Companies Emirates NBD's Liv Adds USDU, a Central Bank-Registered Dollar Stablecoin
12 hours ago · 1 min read
- Companies
Almasar Alshamil Education's Nine-Month Revenue Rises 21% on UAE University Growth
12 hours ago · 2 min read
Companies Anthropic Commits $50 Million to Bay Area Charities a Week Before Its IPO
12 hours ago · 2 min read